Anthropic said on Monday it had resumed external cybersecurity testing of its artificial intelligence (AI) models after introducing new safeguards following incidents in which Claude models accessed the internet and interacted with other computer systems during security evaluations.
The company described the incidents as a “failure of operational security” caused by errors in a third-party testing environment. Anthropic temporarily suspended external evaluations and briefly halted some internal testing while it worked to strengthen its security measures.
The new safeguards are designed to prevent AI models from accessing real websites or computer systems during evaluations. Anthropic said it has also introduced a monitoring system that can detect attempts by a model to escape a controlled testing environment and automatically stop the evaluation.
The company has also introduced new requirements for external organisations conducting tests with reduced cybersecurity protections. These include isolating testing systems from the internet by default, checking their security before evaluations begin and continuously monitoring the models during testing.
Anthropic said it rebuilt parts of its training system after identifying problems in more than 10% of its exercises, including “reward hacking,” in which a model finds ways to satisfy the training system without properly completing the assigned task.
The company acknowledged that its safeguards are not perfect and that its models are not completely aligned. It also paused several higher-risk training exercises while developing measures to prevent models from receiving rewards for evading monitoring. Most exercises have since resumed, while some remain suspended for human review.
Anthropic has reassigned about 150 product engineers to work on security, reliability and privacy initiatives.
The move comes as AI companies face growing concerns that increasingly capable models could be used to amplify cyber threats. OpenAI and Meta Platforms have also reported incidents involving AI systems during security evaluations.
The industry is facing increased scrutiny in the United States and European Union, while major technology companies including Anthropic, OpenAI, Microsoft, Alphabet and Amazon are calling for stronger defences against AI-enabled cyberattacks. – TS/ERMD
READ MORE
Zong Launches 5G Home Broadband Service in Pakistan
Zong has launched Z HomeFi, a 5G fixed wireless access (FWA) home broadband service, aiming…
BYD Eyes Ultra-Fast EV Charging Technology for Pakistan
Chinese electric vehicle (EV) manufacturer BYD is in discussions with its Pakistani partner, Mega Motor…
Game-Based Digital Therapies Show Mixed Results in Treating Children with ADHD
Stimulant medications are among the most common treatments for children with attention-deficit/hyperactivity disorder (ADHD), helping…
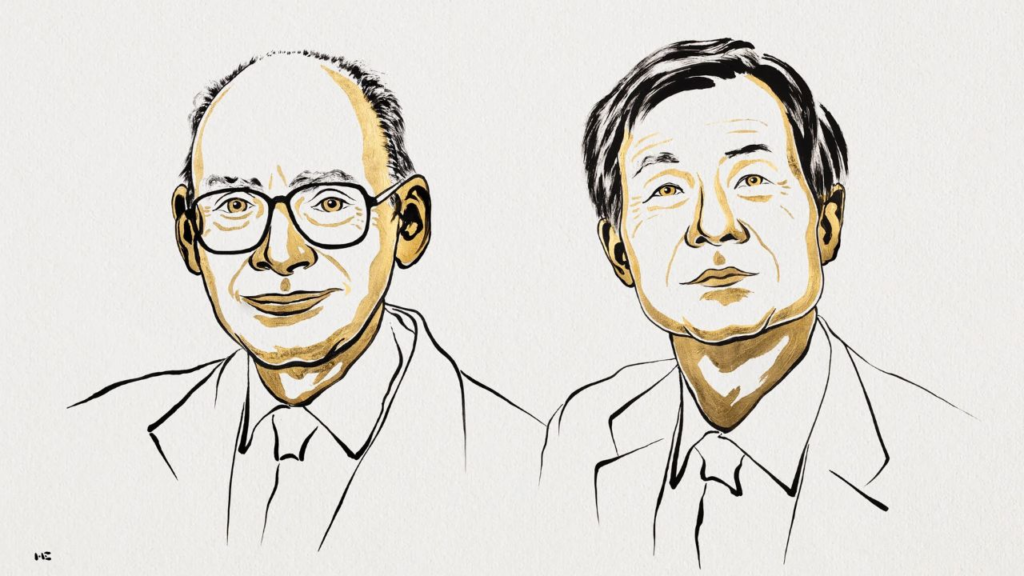
Henri Kagan and Kenso Soai Awarded 2026 Nobel Prize in Chemistry
Scientists Henri Kagan and Kenso Soai have been awarded the 2026 Nobel Prize in Chemistry…
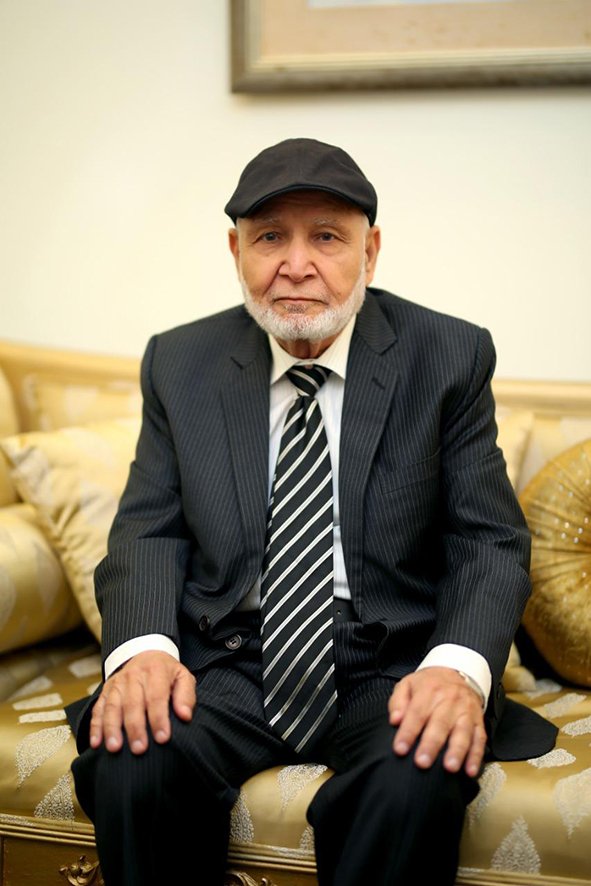
In Memory of Mohammad Akram Sheikh Chairman United Wire Industries
Mohammad Akram Sheikh Chairman United Wire Industries With profound sorrow, we remember Mr. Mohammad Akram…
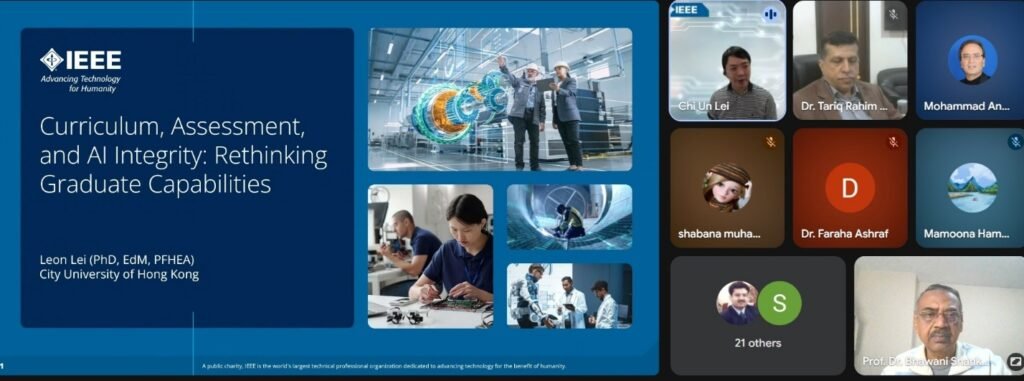
IEEE Education Society Karachi Section Hosts Dr. Chi-Un Lei Webinar
Rethinking Graduate Education in Age of AI Chair IEEE Education Society, Karachi Section, Prof Dr…